Discover what VAPT is, how black-box testing simulates real attackers, and why cloud penetration testing is essential for securing modern, cloud-first businesses.
We still remember a mid-sized company we were consulting for that assumed their web application was "secure enough" until a routine audit uncovered an API misconfiguration that could have exposed customer data. That moment was a wake-up call: how often do organisations equate "we passed a basic scan" with "we are secure"? With cloud adoption accelerating and attackers growing more sophisticated by the month, that assumption can be costly.
What Is VAPT And Why It Matters
When someone asks what VAPT actually is, the answer lies in its two-part structure. VAPT (Vulnerability Assessment and Penetration Testing) pairs a broad, structured vulnerability assessment with targeted, hands-on penetration testing to help organisations find, safely validate, and remediate security weaknesses across systems, networks, and applications.
The vulnerability assessment phase : relies on automated scanning and manual review to flag known weaknesses outdated software, misconfigurations, missing patches, and exposed services.
The penetration testing phase : goes a step further: security testers attempt to exploit those weaknesses in a controlled way, simulating a real-world attacker to see exactly how far a breach could go.
The Growing Need for VAPT in India's Digital Landscape
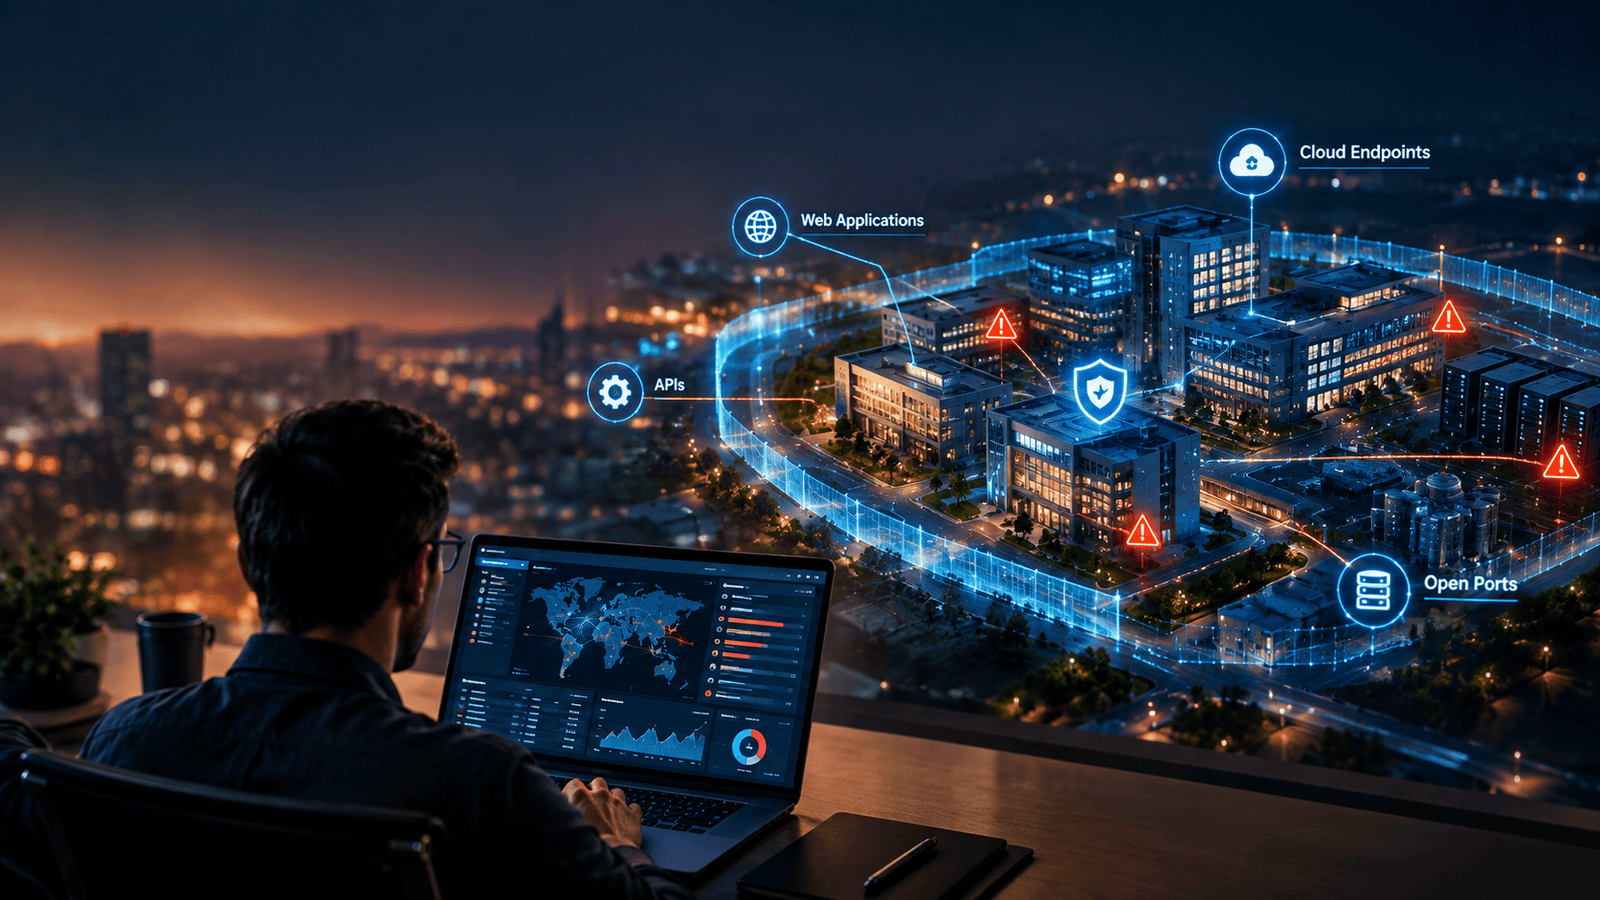
Digital adoption and cloud migration are accelerating across Indian industries, finance, e-commerce, healthcare, manufacturing, and more. Every new SaaS tool, cloud workload, or customer-facing app adds to the attack surface an organisation has to defend.
At the same time, many mid-sized and growing businesses don't have a full in-house security team. Outsourcing VAPT to a specialised partner becomes a cost-effective way to maintain a strong security posture, meet compliance requirements, and protect sensitive data without building an entire security function from scratch something we've explored in more depth in our post on cyber risk management for Indian Businesses.
Understanding Testing Methodologies: Black-Box, White-Box, and Grey-Box
VAPT isn't a one-size-fits-all process different testing methodologies suit different goals and threat models:
Black-Box Testing: Testers have no prior knowledge of the system's internals; no source code, no architecture documents, no credentials. This simulates the view of an outside attacker.
White-Box Testing: Testers have full internal access code, design documents, and configurations enabling a deep review of application logic, data flow, and internal controls.
Grey-Box Testing: A hybrid approach where testers work with partial knowledge, such as limited documentation or a standard user account, simulating a semi-insider threat or a partially informed external attacker.
What Is Black-Box Testing As Used in VAPT
Focusing specifically on black-box testing: this method evaluates a system purely from the outside, without any knowledge of the underlying code, design, or architecture. Testers analyse input/output behaviour, exposed interfaces, and publicly available endpoints to identify vulnerabilities the way a genuine attacker would find them.
Enter the Cloud Era: Why Cloud Penetration Testing Is Unique
As organisations move infrastructure and applications to the cloud, new categories of risk emerge. Virtual machines, storage buckets, dynamic auto-scaling, containerisation, APIs, and identity and access management (IAM) all combine to expand the attack surface and traditional, on-premise-style VAPT has to evolve to keep up.
This is where a dedicated cloud penetration test becomes essential. It examines cloud-specific risk factors IAM misconfigurations, insecure default settings, exposed services, misconfigured storage buckets, and network exposure across your cloud environment. Cloud pen testing helps ensure that deployments spanning public and private resources, elastic scaling, and third-party infrastructure stay secure and properly isolated, preventing data leaks, privilege escalation, or misuse of cloud resources.
How VAPT, Black-Box Testing, and Cloud Penetration Testing Work Together
A comprehensive security evaluation typically brings all three together for maximum coverage:
Start with a vulnerability assessment broad : scanning across networks, applications, and services to build a baseline picture of known weaknesses.
Run black-box testing : to simulate external attacks against exposed assets, such as web apps, APIs, and public-facing endpoints.
For cloud-hosted infrastructure, perform a cloud penetration test : reviewing IAM, storage, network, and container or VM configurations for cloud-specific threats.
Compile and prioritise findings : by severity and exploitability, then build a remediation plan around the highest-risk issues first.
Challenges and Limitations: What VAPT and Cloud Pen Testing Can't Always Catch
Even thorough VAPT, black-box testing, and cloud penetration testing have inherent limits worth knowing:
Narrow scope leaves gaps : If testing covers only the web app or only the network, other assets, third-party services, internal APIs, and database servers can be missed entirely.
Cloud environments are dynamic : Instances, containers, storage, and IAM policies change constantly; what was secure during last quarter's test may not be secure today.
Some flaws simply evade testing : Zero-day bugs and logic flaws that only appear under specific conditions can slip past both scanning and manual testing.
Human factors sit outside VAPT's scope : Misconfigurations, policy lapses, weak operational security, and social engineering risks often require separate controls, which is why security awareness training and layered data loss prevention matter just as much as technical testing. We've written more about this in how to protect your company's data from accidental loss or leaks.
Best Practices: How We Recommend Implementing VAPT and Cloud Security
Based on industry standards and what we've seen work in practice:
Define a clear scope and objective : identify exactly which assets will be tested: applications, APIs, cloud infrastructure, storage, and so on.
Combine automated scanning with manual testing : automated tools catch known issues quickly; manual, expert-driven testing uncovers complex or chained vulnerabilities that scanners miss.
Test regularly, not just once : especially for cloud environments, retest after every major deployment, update, or infrastructure change.
Prioritise remediation by impact : fix high-severity, high-exploitability issues first, and pair this with prompt patching and least-privilege access controls.
Bake in cloud security hygiene : encryption by default, secure configuration baselines, strong IAM practices, network segmentation, minimal public exposure, and regular audits.
Key Takeaways
VAPT combines vulnerability assessment (finding weaknesses) with penetration testing (safely exploiting them) to reveal what's actually exploitable, not just theoretically risky.
Black-box testing simulates a real external attacker with zero inside knowledge, exposing what your organisation looks like from outside the perimeter.
Cloud penetration testing targets risks unique to cloud environments IAM misconfigurations, exposed storage, insecure defaults that traditional network testing often misses.
The most effective security programs layer all three together, then prioritise remediation by severity and exploitability.
Even solid VAPT and cloud testing programs have blind spots narrow scope, dynamic cloud changes, zero-days, and human error still need separate controls like awareness training and data loss prevention.
Testing should be continuous, not one-off retest after every major deployment, update, or infrastructure change.
Frequently Asked Questions
1. What is VAPT in simple terms?
VAPT stands for Vulnerability Assessment and Penetration Testing. It's a two-step process: first scanning your systems to find known weaknesses, then safely attempting to exploit those weaknesses to see how serious they really are.
2. What's the difference between black-box, white-box, and grey-box testing?
Black-box testing gives testers zero internal knowledge, simulating an outside attacker. White-box testing gives testers full access to code and architecture for a deep internal review. Grey-box testing sits in between, using partial knowledge such as limited credentials.
3. Why do I need a separate cloud penetration test if I already do regular VAPT?
Traditional VAPT is often built around on-premise networks and applications. Cloud environments introduce unique risks IAM misconfigurations, exposed storage buckets, insecure default settings that a cloud-specific test is designed to catch.
4. How often should VAPT and cloud penetration testing be done?
At minimum, annually, but more frequent testing is recommended after major deployments, infrastructure changes, or significant updates, especially in fast-changing cloud environments.
5. Can VAPT and cloud pen testing catch every possible vulnerability?
No. Narrow scoping, constantly changing cloud configurations, zero-day flaws, and human error (like social engineering or policy lapses) can all fall outside the scope of a single testing engagement. That's why testing should be paired with ongoing monitoring, awareness training, and data protection controls
6. Is VAPT only relevant for large enterprises?
No , mid-sized and growing businesses are often more exposed, since they typically lack dedicated in-house security teams. Outsourcing VAPT is a practical, cost-effective way to close that gap.Ready to find out where your real exposure lies? Delphi Infotech about a tailored VAPT and cloud penetration testing engagement for your environment.