Pen testing services help Indian organisations undergoing DPDP Act compliance enhance enterprise risk management and data security.
Here's a question worth sitting with for a second: if an attacker got into your network right now and just... stayed quiet for six months, would you know? Most Indian enterprises can't honestly say yes. And that gap, the not knowing, is basically the reason for penetration testing services.
Digital transactions are exploding. Cloud adoption isn't slowing down. Vendor networks keep sprawling wider every year. Somewhere in all that growth, the line between “a cybersecurity incident” and “a full-blown business crisis” quietly disappeared. This article shows how effective penetration testing impacts enterprise risk management. It explains why data security is now a boardroom topic, not just an IT issue. It also highlights what Indian organisations must do as new regulations come into play.
Why Cyber Risk Has Become a Boardroom Priority in India
Not that long ago, cyber risk lived quietly at the bottom of the IT department's quarterly report. Nobody outside the tech team read it closely. That's changed, and changed fast. Cyber risk is now on the board's radar, alongside currency exposure and supply chain disruption. The numbers back this up. Cyberattacks on Indian companies are rising over 25% each year. This trend is a key reason why cybersecurity is no longer just "an IT thing." It has become a vital part of enterprise risk management.
The threat data tells the same story from a different angle. Seqrite's 2026 India Cyber Threat Report noted over 156 million malware detections in businesses from October 2025 to May 2026.Trojans and file infectors were the main offenders. Ransomware activity remained high in both cloud and on-premise systems.
What Penetration Testing Services Actually Test
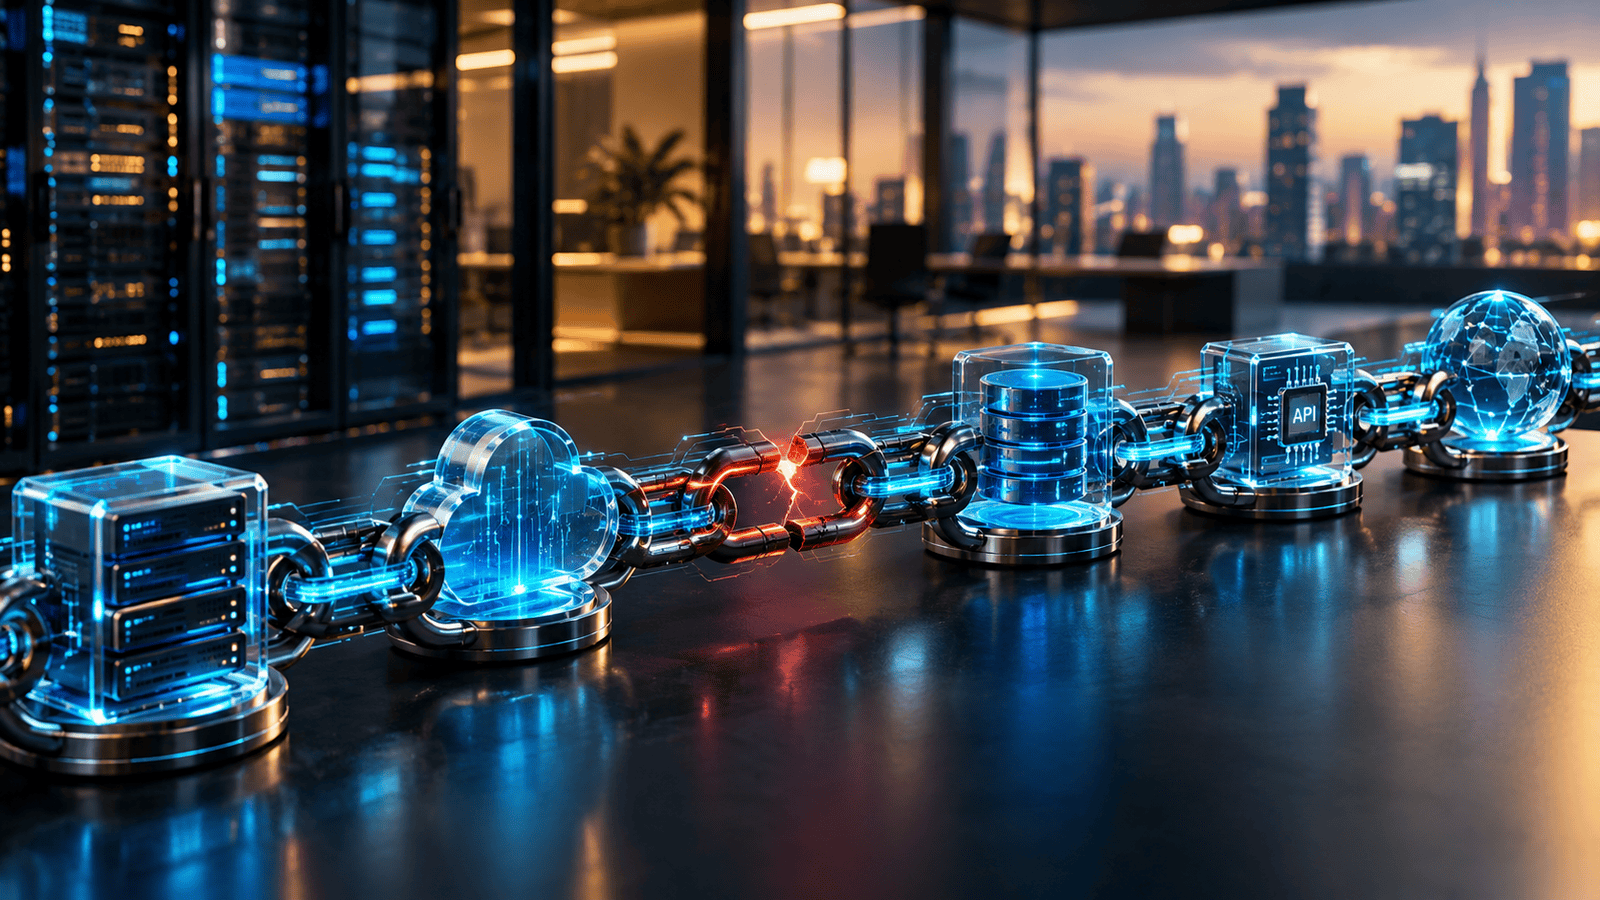
Let's be plain about what a penetration test actually is: a controlled, fully authorised simulation of a real attack, run by people who are paid to think like attackers. That's the whole job. A decent tester won't just run a scan and hand you a list of known flaws; that's what automated tools already do. Instead, they string small weaknesses together. A misconfigured server here. A password someone reused. An API endpoint that's a little too exposed. Individually, none of these seem urgent. Chained together, they're exactly how a real breach happens.
The Business Case for Investing in Regular Penetration Testing
There was a time when penetration testing was something only banks and big IT firms cared about. That time is over. The penetration testing market in India is set to grow from about USD 68.6 million in 2025 to nearly USD 185 million by 2030. This marks a CAGR of around 18%, which is much higher than the global growth rate.
Regulation is doing a lot of the pushing here. The RBI's 2023 circular says that regulated payment system operators and urban cooperative banks must do annual cyber risk assessments. This includes penetration testing. One circular, and suddenly, a huge chunk of the financial sector had a formal testing schedule to follow.
But even without the regulatory push, the maths works out. One serious breach can lead to fines, customer loss, and repair costs. These can make an annual testing budget seem small. This is especially true in BFSI. The high volume of transactions makes these organisations prime targets for fraud. Simply put: testing before an attacker finds the gap is a lot cheaper, than handling the fallout once they do.
How Enterprise Risk Management Is Evolving Beyond Compliance Checklists
For years, enterprise risk management in India basically meant a spreadsheet. A static risk register, dusted off once a year, reviewed by internal audit, then filed away until next year. That model is fading, and fast. Organisations are shifting towards cloud- ERM platforms. These platforms give them real-time dashboards and predictive analytics. The use of these tools is increasing by more than 30% each year. Organisations are shifting towards cloud- ERM platforms. These platforms give them real-time dashboards and predictive analytics. The use of these tools is increasing by, than 30% each year.
Where Data Security Sits Inside a Modern Risk Framework
Data security used to get filed under "IT risk" and left there to gather dust. That's not really how it works anymore. In a risk framework data securityacts like connective tissue. It ties into risk, reputational risk, legal risk and operational risk all at once. It doesn't stand alone. It connects everything. This kind of interdependence means that a problem, in data security can quickly ripple across areas. That’s why treating data security as an IT issue is a mistake. It’s not about protecting data. It’s about protecting the organization. The way data security fits into risk management shows how everything is connected. You can't ignore one part without affecting the others.
The DPDP Act, 2023 and What It Demands From Data Fiduciaries
India's data protection rules have gone from talked-about to real, and quickly. The Digital Personal Data Protection Rules, 2025 were formally notified on 13 November 2025. That notification established the Data Protection Board of India. It also laid out a phased compliance timeline. The heavier obligations like consent, notice, security safeguards, and breach reporting will start in 18 months.
Under these rules, organisations classified as data fiduciaries must implement security safeguards. These include encryption, access controls, and ongoing monitoring. These are standard measures that any responsible organisation should follow. They also have to tell the Data Protection Board within 72 hours of discovering a personal data breach. In addition they must inform the individuals whose data was exposed.
Here’s where it gets complicated: this new requirement sits on top of India’s existing CERT-In guidelines. Those guidelines already require certain cybersecurity incidents to be reported within six hours. So after one incident happens a company might end up juggling two reporting timelines at the same time. One clock ticks every six hours the every 72
The penalties? They’re not small. They can go into hundreds of crores of rupees. That’s why security testing is no longer something you do because its good practice. It’s now directly tied to compliance. Risk documentation has moved from being a to-have to a must-have. This shift means companies can no longer treat cybersecurity as something, from their legal obligations. It's part of the core responsibility now.
Connecting Penetration Testing Results to Enterprise Risk Registers
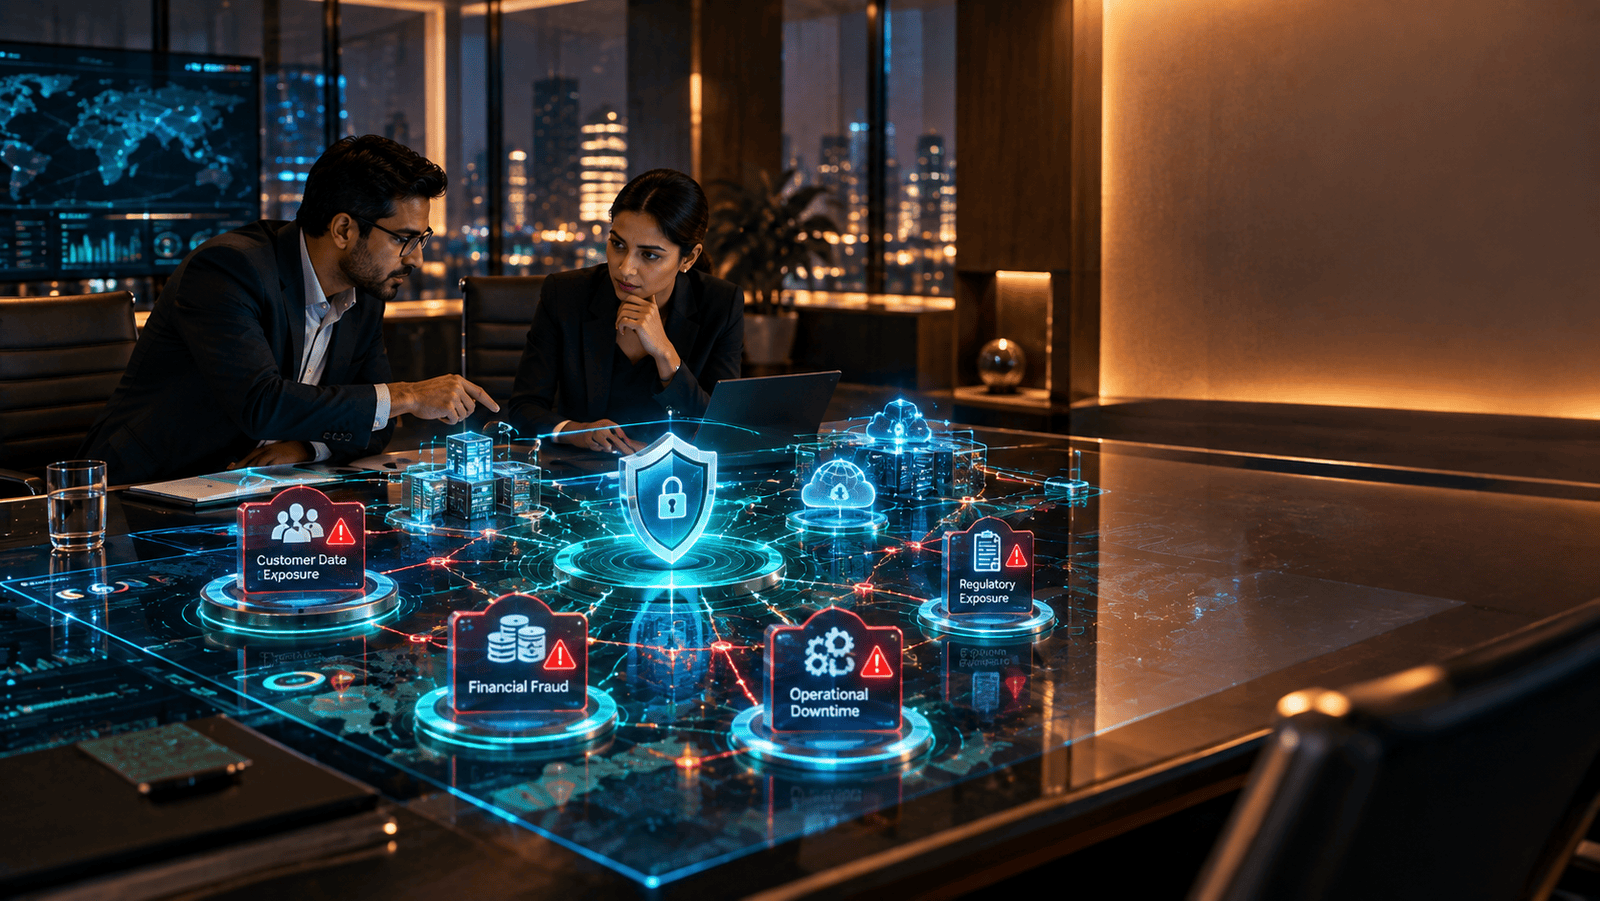
A penetration test report is only worth so much sitting in someone's inbox. The true value comes when results are added to the enterprise risk register, not just left in a PDF for the security team. This means connecting each vulnerability found during testing to a business risk. For example, risks could include customer data exposure, payment fraud, service outages, or regulatory fines.Then, it’s important to assign that risk to someone outside the security team to manage. A business unit must take responsibility.head. A compliance officer. Sometimes a vendor manager, if that's where the risk actually sits.
Risk committees can track issues like other risks. They assess likelihood, potential damage, and time needed for resolution. Regulators and auditors now expect this kind of record. It demonstrates the "reasonable security safeguards" needed by frameworks like the DPDP Rules. Companies that see a testing report as a one-time task often face the same problems in future audits. This can happen year after year.
Industry-Specific Risk Priorities: BFSI, Healthcare, and IT/ITES
Not every sector faces the same risks, so a good testing programme shouldn't run the exact same checklist everywhere.
BFSI must balance RBI mandates on one side with a volume of digital transactions on the other side, which makes fraud prevention and payment system integrity the obvious priority.
Network and application testing here tends to cluster around core banking and payment infrastructure
Healthcare has changed a lot. Patient records and telemedicine platforms grow quickly, often outpacing security measures. Legacy systems were created long before we understood modern threats. This mix makes data security assessments and access control reviews crucial.
In IT and ITES, which are key to India's outsourcing economy, exposure often comes from subcontracting and high staff turnover. These factors lead to supply chain and insider-risk issues. Even large, secure firms may face problems because smaller vendors are so integrated into their operations.
The key lesson in every sector is clear: shape your testing scope around where attackers focus in that industry. Avoid using a one-size-fits-all template.
Building an Internal Culture of Security and Risk Awareness
None of this matters much if the people around the technology aren't ready. Human behaviour and workforce governance are now as important to enterprise risk as the technical side. This includes everything from phishing risks and password hygiene to how carefully employees use the AI tools they work with daily.
Choosing a Penetration Testing and Risk Management Partner
Picking the right partner matters nearly as much as deciding to test at all. Check for methods linked to trusted frameworks. Find testers with verifiable credentials. Also, look for someone who can explain technical results in a way that a risk committee or board will truly grasp.
Key Takeaways
Cyberattacks on Indian businesses have increased by over 25% each year. This shift has moved cybersecurity from being just an IT issue to a key risk priority for the whole enterprise.
Penetration testing mimics real attacker behaviour to find weaknesses. It’s most helpful when findings are turned into risk language and added to the enterprise risk register.
India's penetration testing market is growing quickly. This growth is mainly due to regulatory rules, such as the RBI's 2023 circular for banks and payment system operators.
The DPDP Rules, 2025, require the Data Protection Board to notify of breaches within 72 hours. This adds to CERT-In's 6-hour reporting rule. Now, there are two overlapping timelines for compliance after an incident.
Enterprise risk management is moving from yearly checklists to continuous, integrated governance platforms.
Risk priorities should focus on specific sectors. For instance, fraud in BFSI, patient data in healthcare, and supply chain exposure in IT/ITES need attention. These factors should guide the testing programme's scope.
Workforce awareness and insider-risk controls matter just as much as the technical safeguards.
Frequently Asked Questions
How often should an Indian enterprise conduct penetration testing?
A : Most regulated entities, RBI-regulated payment operators and banks included, need to test at least once a year. If your organisation ships code often, uses the cloud regularly, or makes big infrastructure changes, it’s a good idea to test more often. New deployments often introduce hidden vulnerabilities between scheduled cycles.
What's the difference between a vulnerability scan and a penetration test?
A : A vulnerability scan is automated. It checks your systems against a database of known weaknesses and flags matches. A penetration test goes deeper. Real people exploit and link vulnerabilities like actual attackers do. This approach uncovers risks that automated scans often miss.
Does the DPDP Act require penetration testing specifically?
A :Not by name. The DPDP Rules require data fiduciaries to use "reasonable security safeguards." They don't specify penetration testing as a must. However, having a tested and monitored security approach is viewed as solid evidence that you’re fulfilling this duty. This is especially true if the Data Protection Board investigates a breach at your organisation.
4 . Which industries in India face the highest cybersecurity risk?
A: BFSI, healthcare, and IT/ITES currently face the highest exposure. BFSI is targeted for payment fraud given the volume of digital transactions it processes, healthcare holds highly sensitive patient data often on legacy systems, and IT/ITES firms inherit supply chain risk from the subcontracting arrangements common in India's outsourcing sector.
Identify vulnerabilities before attackers do. Partner with Delphi Infotech for penetration testing and data security solutions that strengthen your cyber resilience.